(Modified:
2026-06-28)
— Written by
SimeonOnSecurity— 5 min read
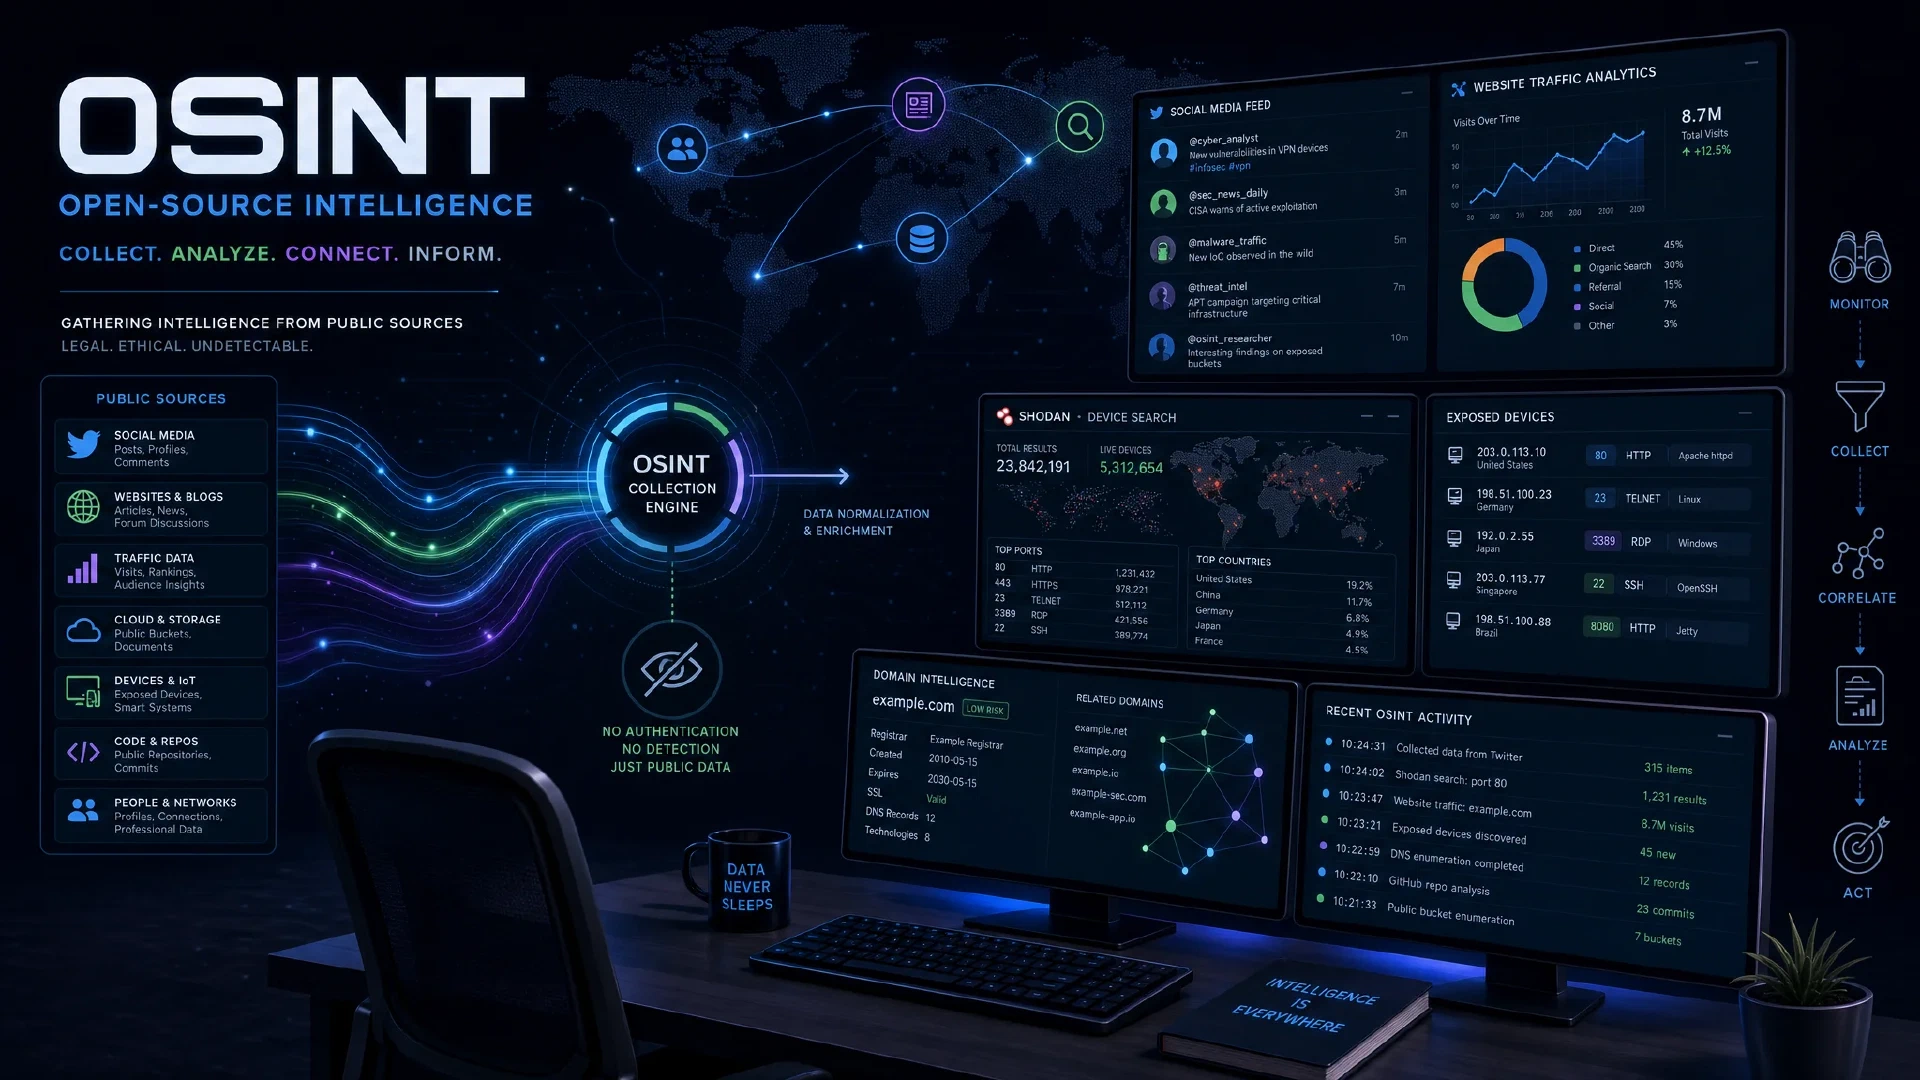
Master reconnaissance and enumeration for the CompTIA PenTest+ PT0-003 exam. Learn OSINT, active and passive recon, enumeration techniques, secrets discovery, and the right tools.
(Modified:
2026-06-26)
— Written by
SimeonOnSecurity— 5 min read
Learn to automate OSINT with the Shodan PowerShell Modules collection, which provides an interface to interact with the Shodan API for various functions such as hostname resolution, exploit searching, and more.
An online tool to perform a Shodan IP lookup. Retrieve information such as hostnames, open ports, tags, CPEs, and vulnerabilities associated with an IP address.