Analyze Kerberos service-ticket exposure, account privilege, encryption choices, and delegation evidence with a domain escalation review record.
Module 16: separate ticket exposure from account authority #red team
#red team course
Plan lateral movement with explicit name resolution, authentication, authorization, service, and rollback evidence instead of assuming every credential reaches every host.
Module 17: prove each movement prerequisite before crossing a host boundary #red team
#Lateral Movement
#SSH
#authentication
#red team course
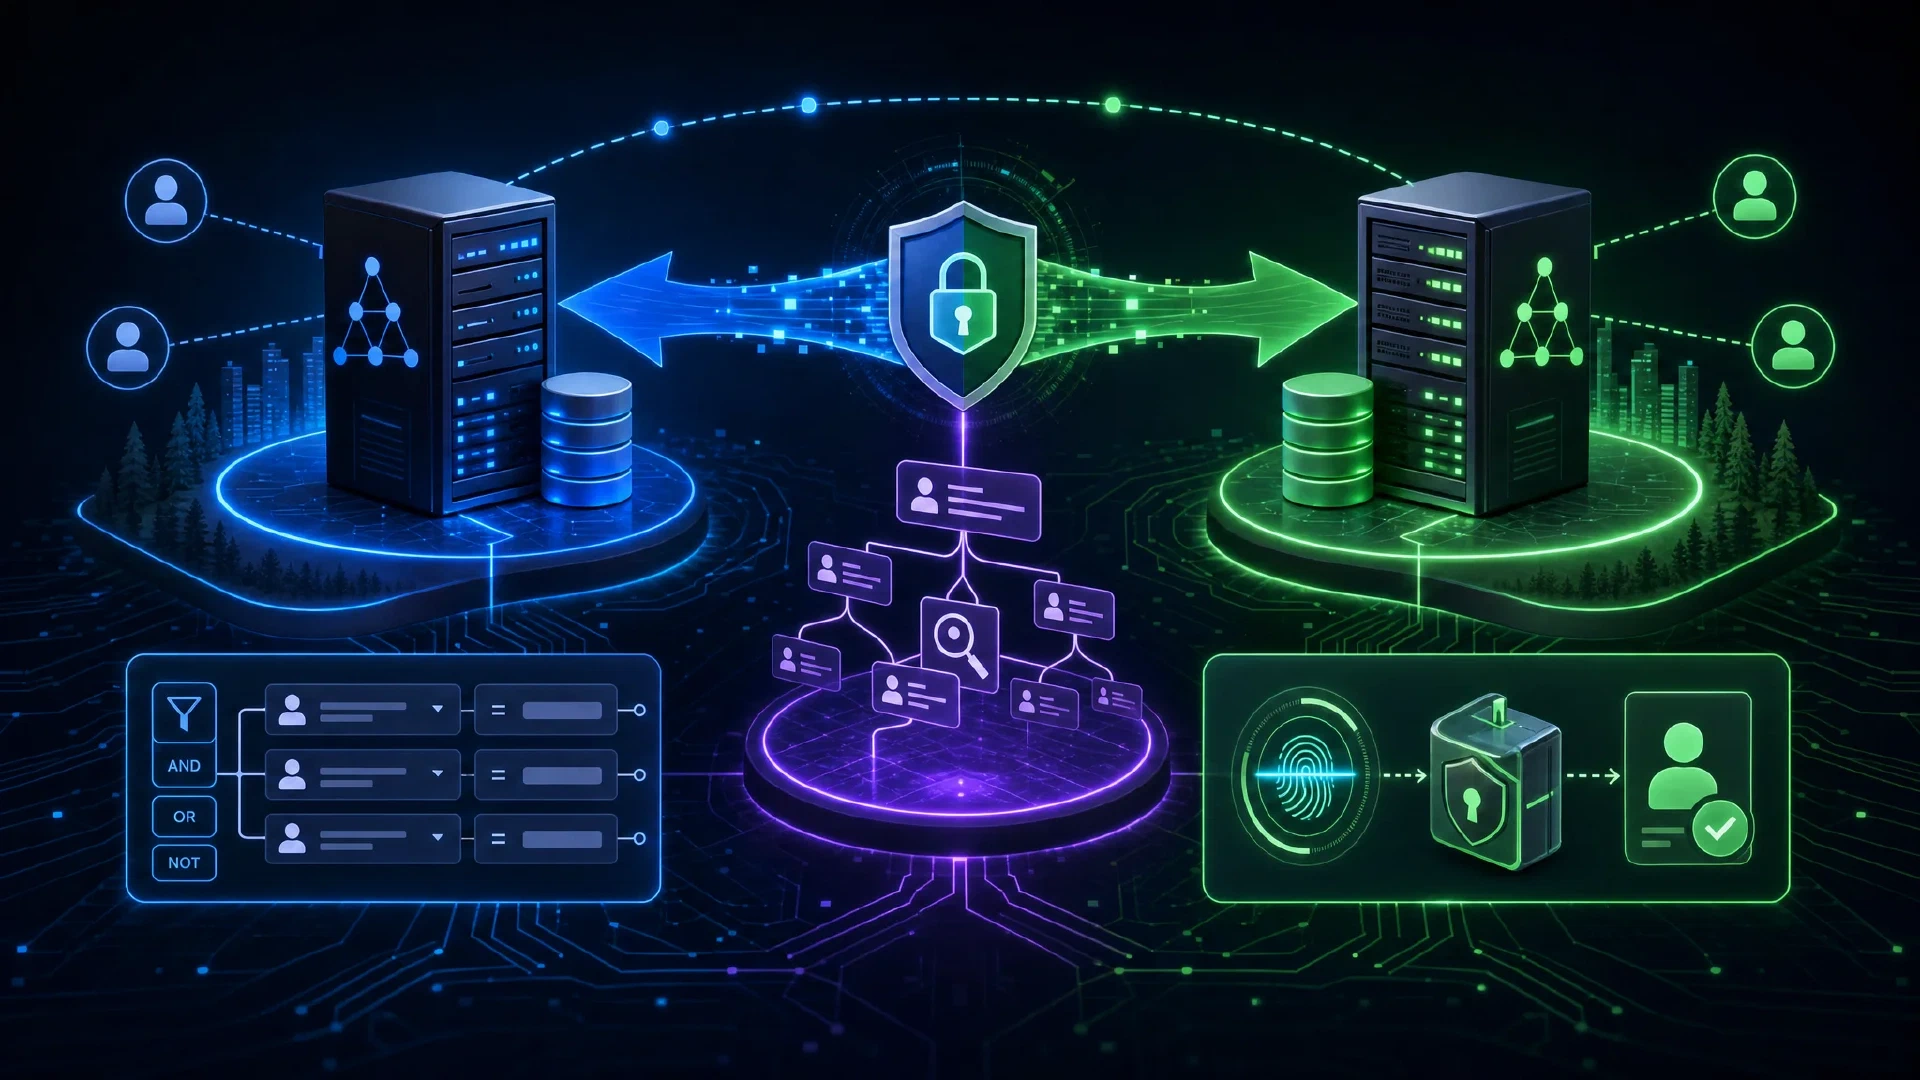
Analyze trust direction, selective authentication, SID filtering, LDAP scope, and query results with a cross-domain pivot decision record.
Module 18: treat a trust as a relationship to test, not a shortcut #red team
#enumeration
#red team course
Design bounded red-team access with expiry, ownership, redundancy, failover, and operator records that remain useful during a live assessment.
Module 19: make access bounded, owned, and recoverable #red team
#Access control
#red team course
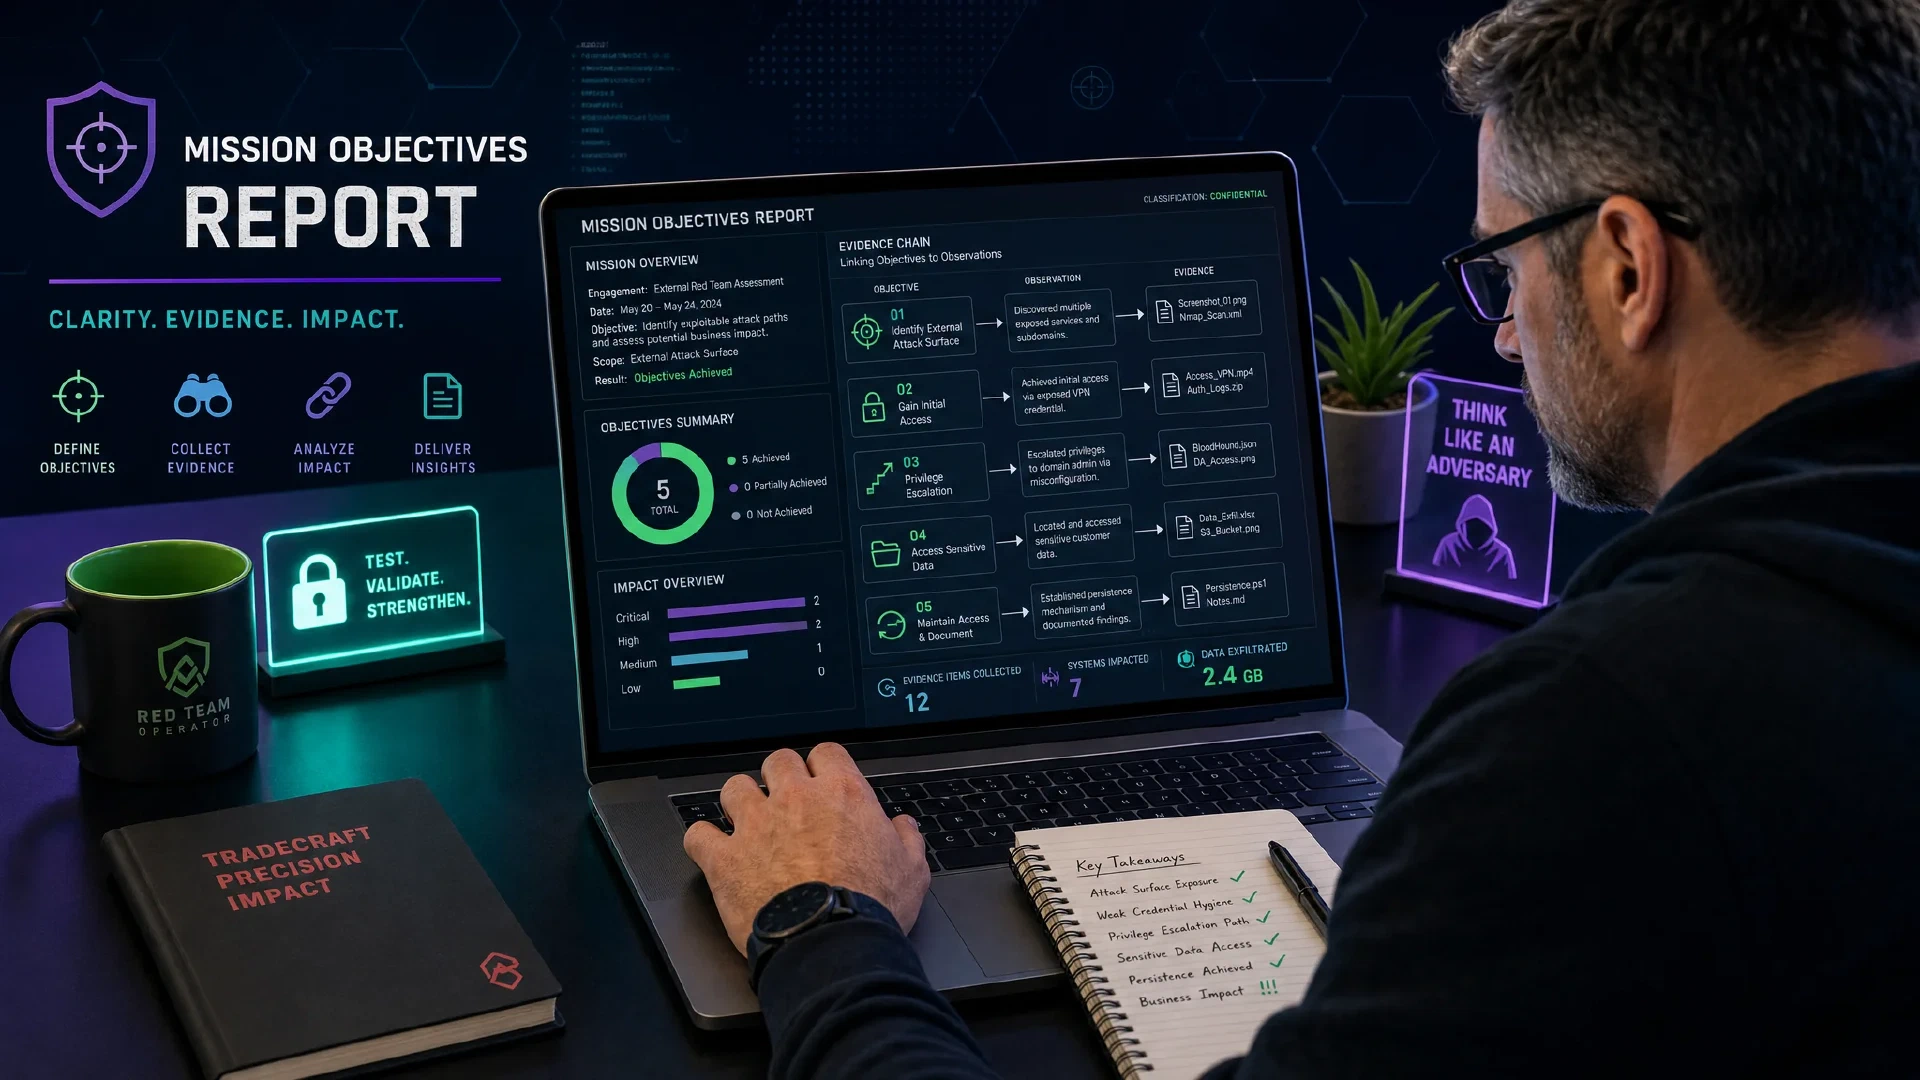
Turn red-team objectives into bounded tests and evidence-backed findings with explicit limits, remediation owners, and retest conditions.
Module 20: make the final report useful to the next decision maker #red team
#reporting
#red team course