Build a current host-state record using Windows and Linux identity, process, socket, and routing evidence, with a worked snapshot comparison.
Module 11: identify the host context and know when observations become stale. #red team
#post exploitation
#red team course
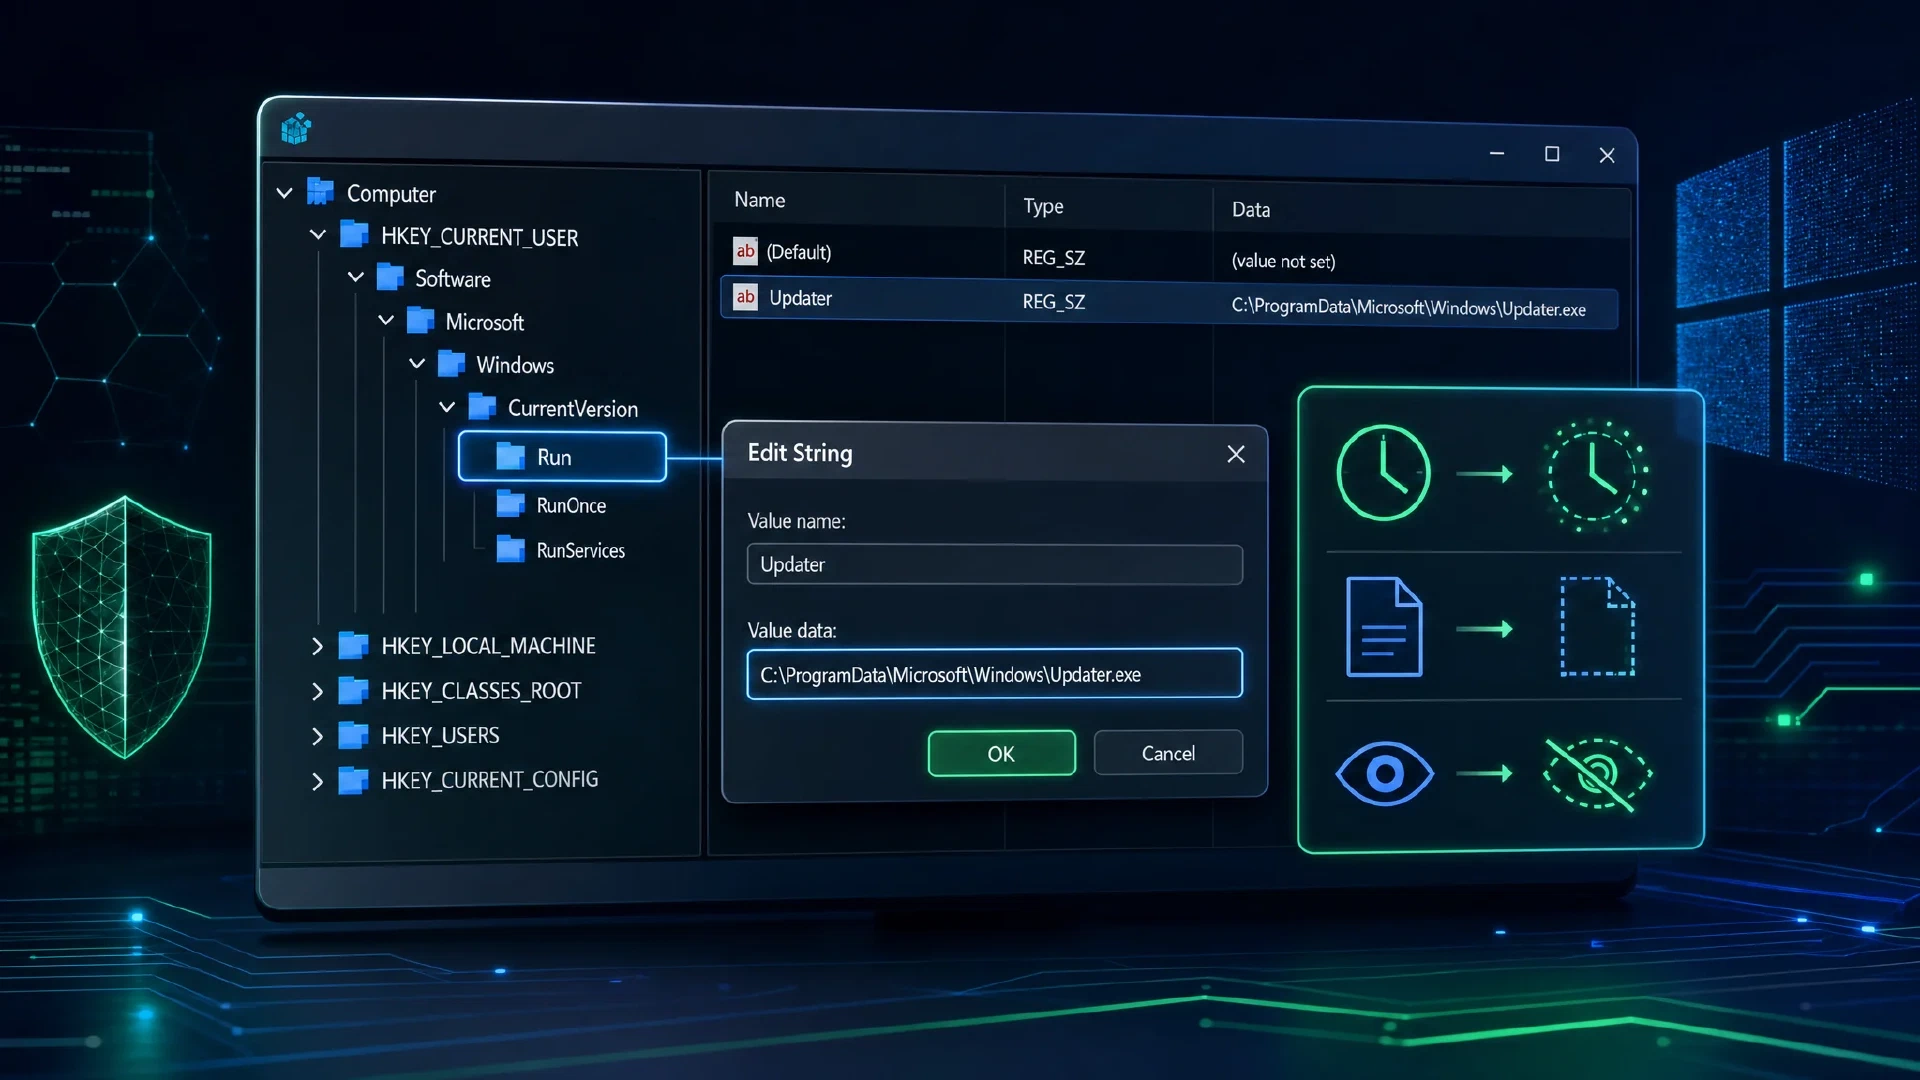
Understand user startup triggers, HKCU context, and restoration. Follow a benign Notepad Run-entry lab with evidence and cleanup checks.
Module 12: verify the trigger, execution, and complete restoration. #red team
#red team course
Evaluate Windows privilege escalation paths through service permissions, DLL loading, evidence quality, and a read-only lab exercise.
Module 13: establish the permission boundary before claiming escalation #red team
#privilege escalation
#red team course
Understand Windows service persistence, process lifetime, architecture, and migration tradeoffs through read-only inspection and a service lifecycle exercise.
Module 14: distinguish service configuration from process execution and durability #red team
#red team course
Restore persistence changes with a precise artifact ledger, correct registry identity, evidence preservation, and independent verification of cleanup.
Module 15: restore owned changes and preserve evidence for review #red team
#red team course