Understand BOF file formats, architecture compatibility, client integration, runtime limits, and failure boundaries through a benign test design.
Module 6: understand the execution boundary and its consequences. #red team
#Cobalt Strike
#red team course
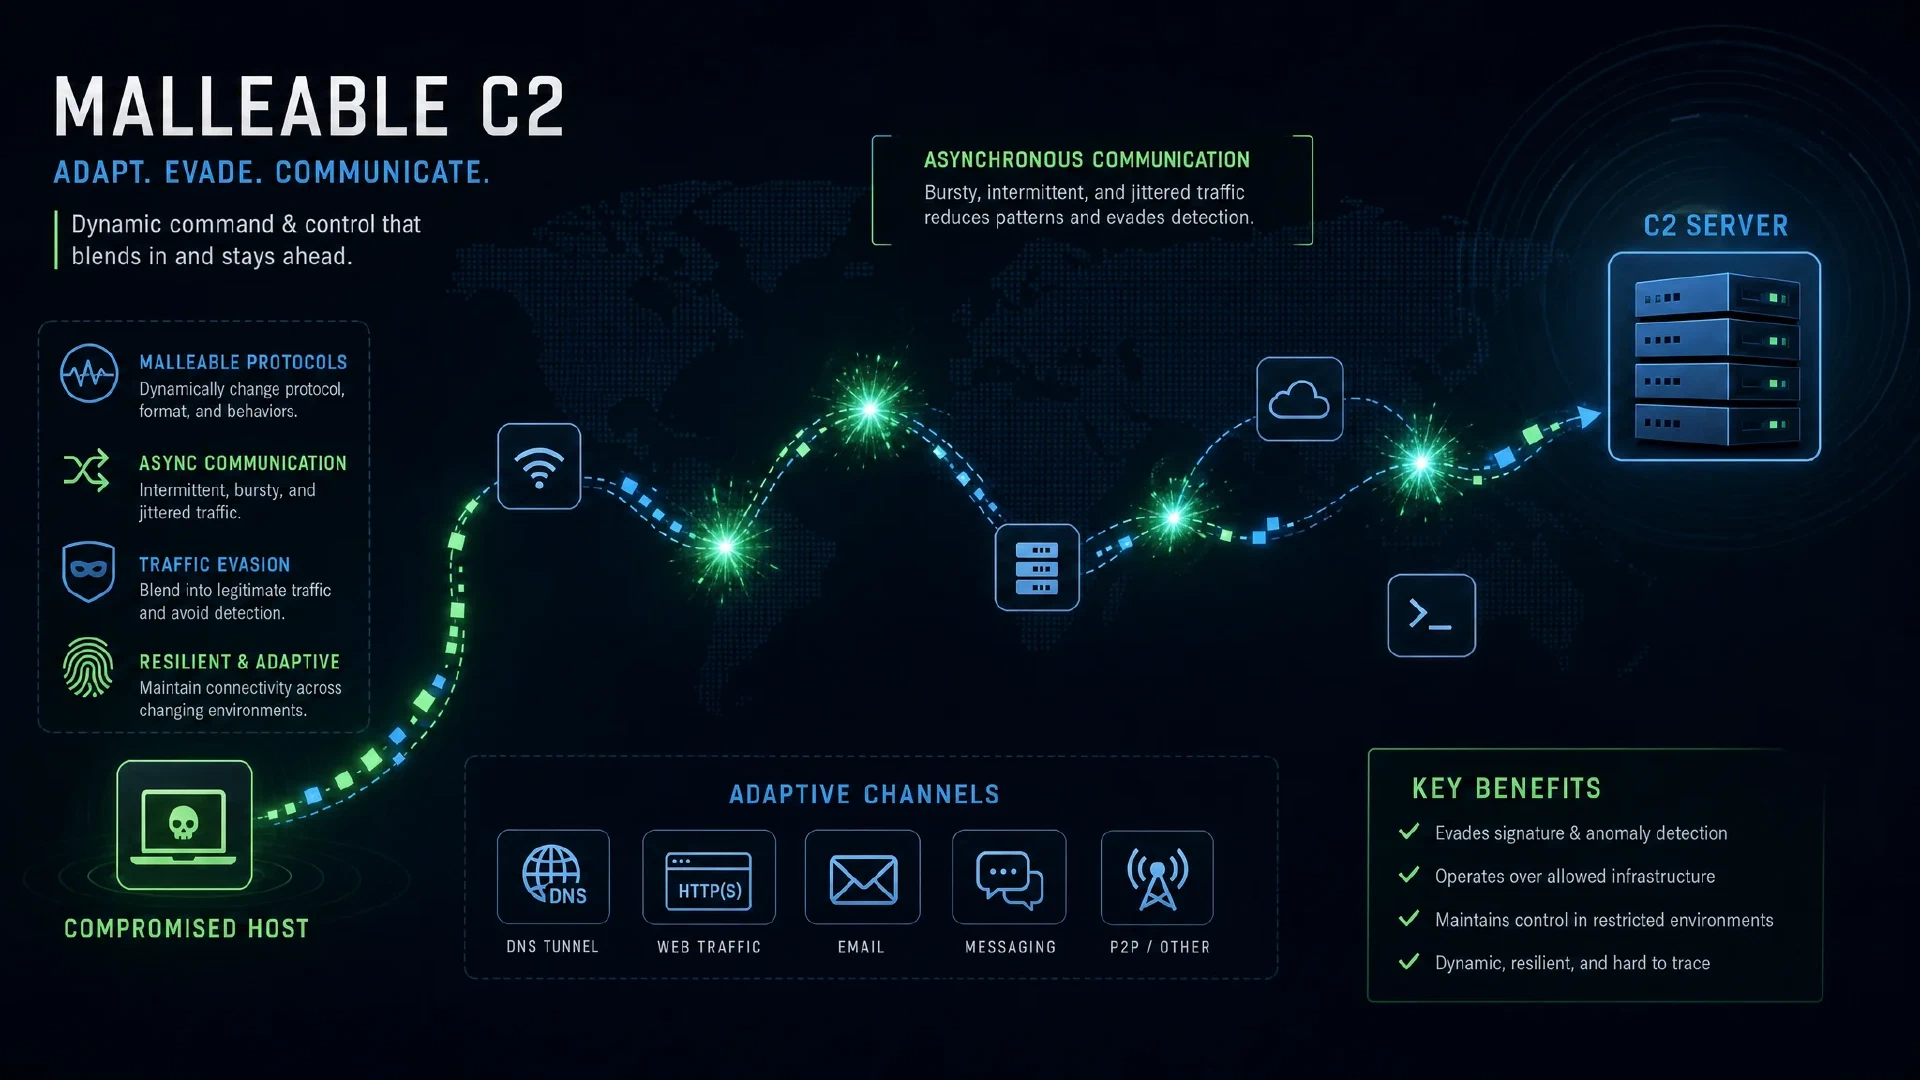
Separate profile validity, working communication, telemetry, and detection with a local HTTP exercise and controlled comparison record.
Module 7: measure communication behavior and support detection claims. #red team
#Cobalt Strike
#red team course
Evaluate public sources, RDAP, DNS, certificate logs, and scan data. Build a traceable OSINT brief with worked examples and source-quality checks.
Module 8: turn public observations into supported decisions. #red team
#OSINT
#Shodan
#red team course
Interpret Nmap port states, scan methods, and vantage points through a loopback exercise, segmentation case, and evidence-based scan plan.
Module 9: connect scan observations to supported conclusions. #red team
#nmap
#red team course
Distinguish phishing delivery, interaction, execution, and access. Interpret campaign metrics, modern Office controls, and Windows architecture with worked examples.
Module 10: measure the boundary each initial-access test exercises. #red team
#phishing
#Cobalt Strike
#HTTPS
#red team course