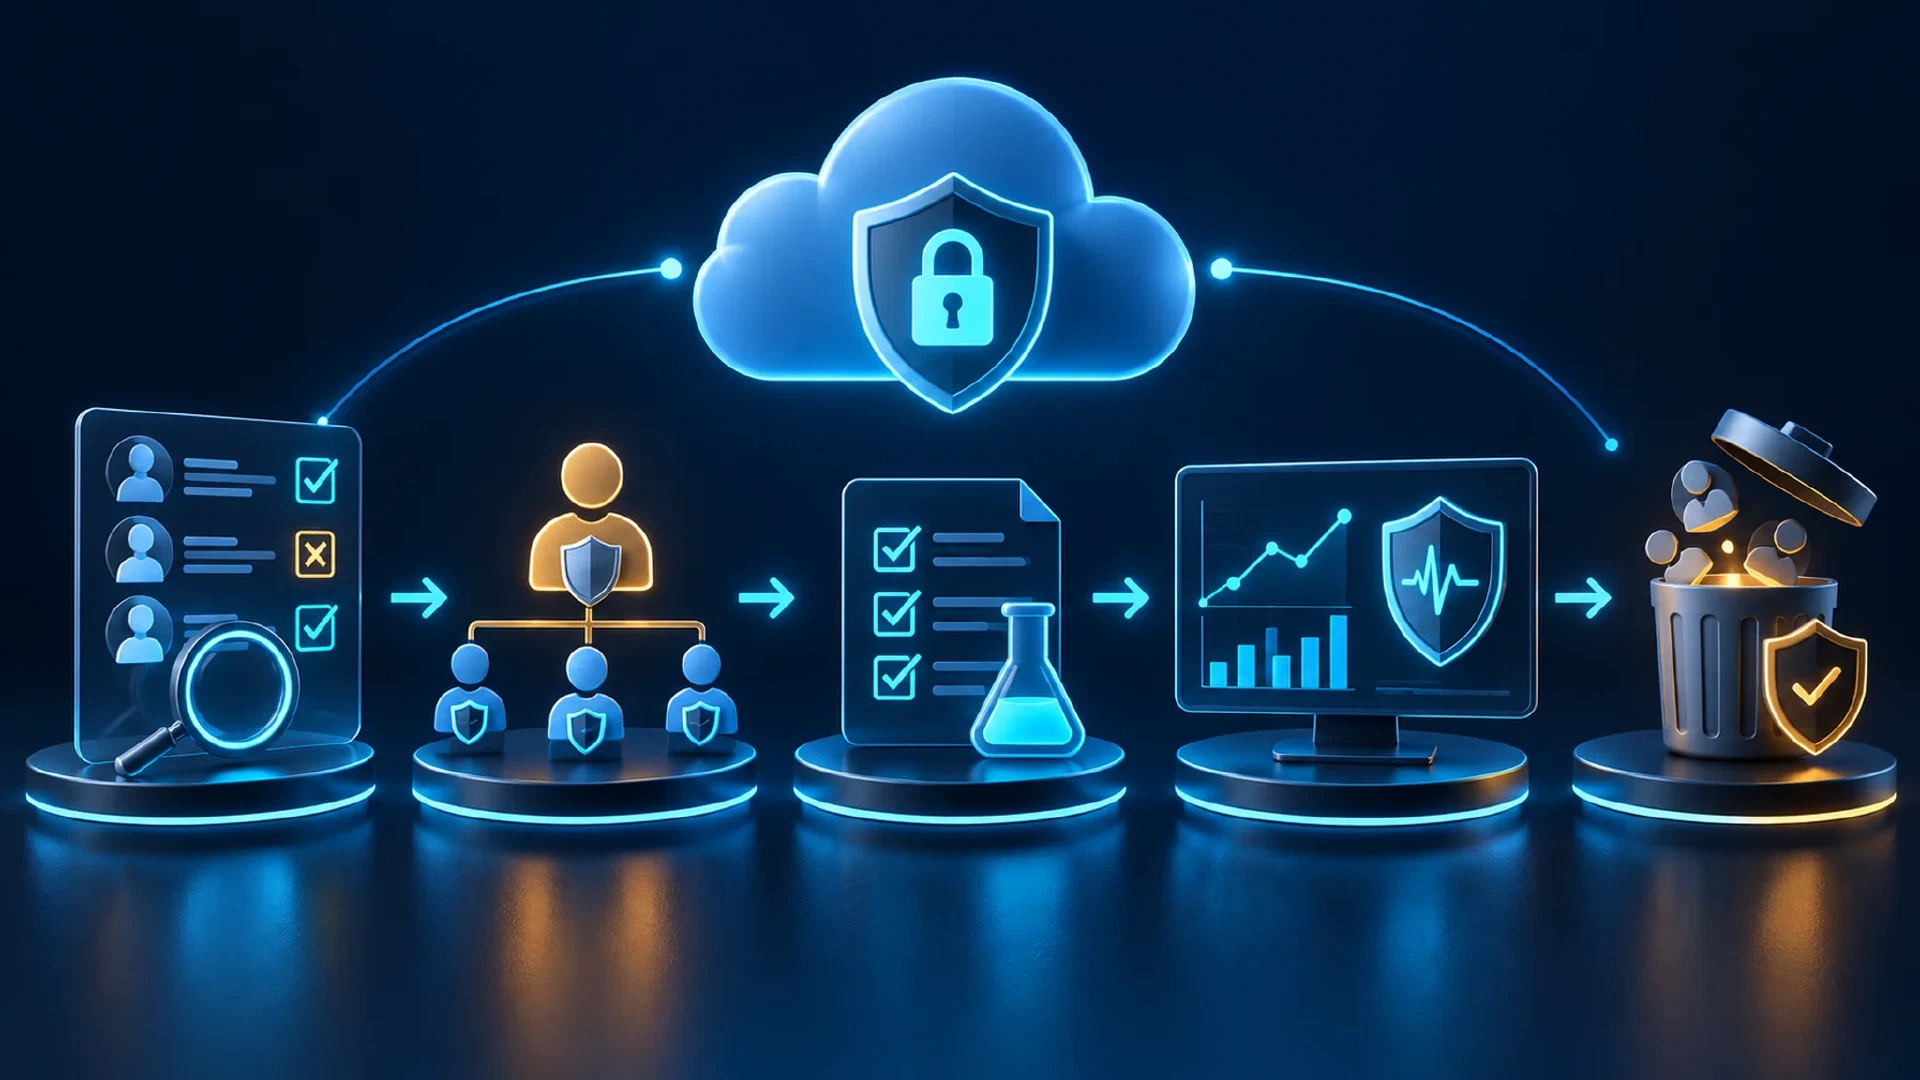
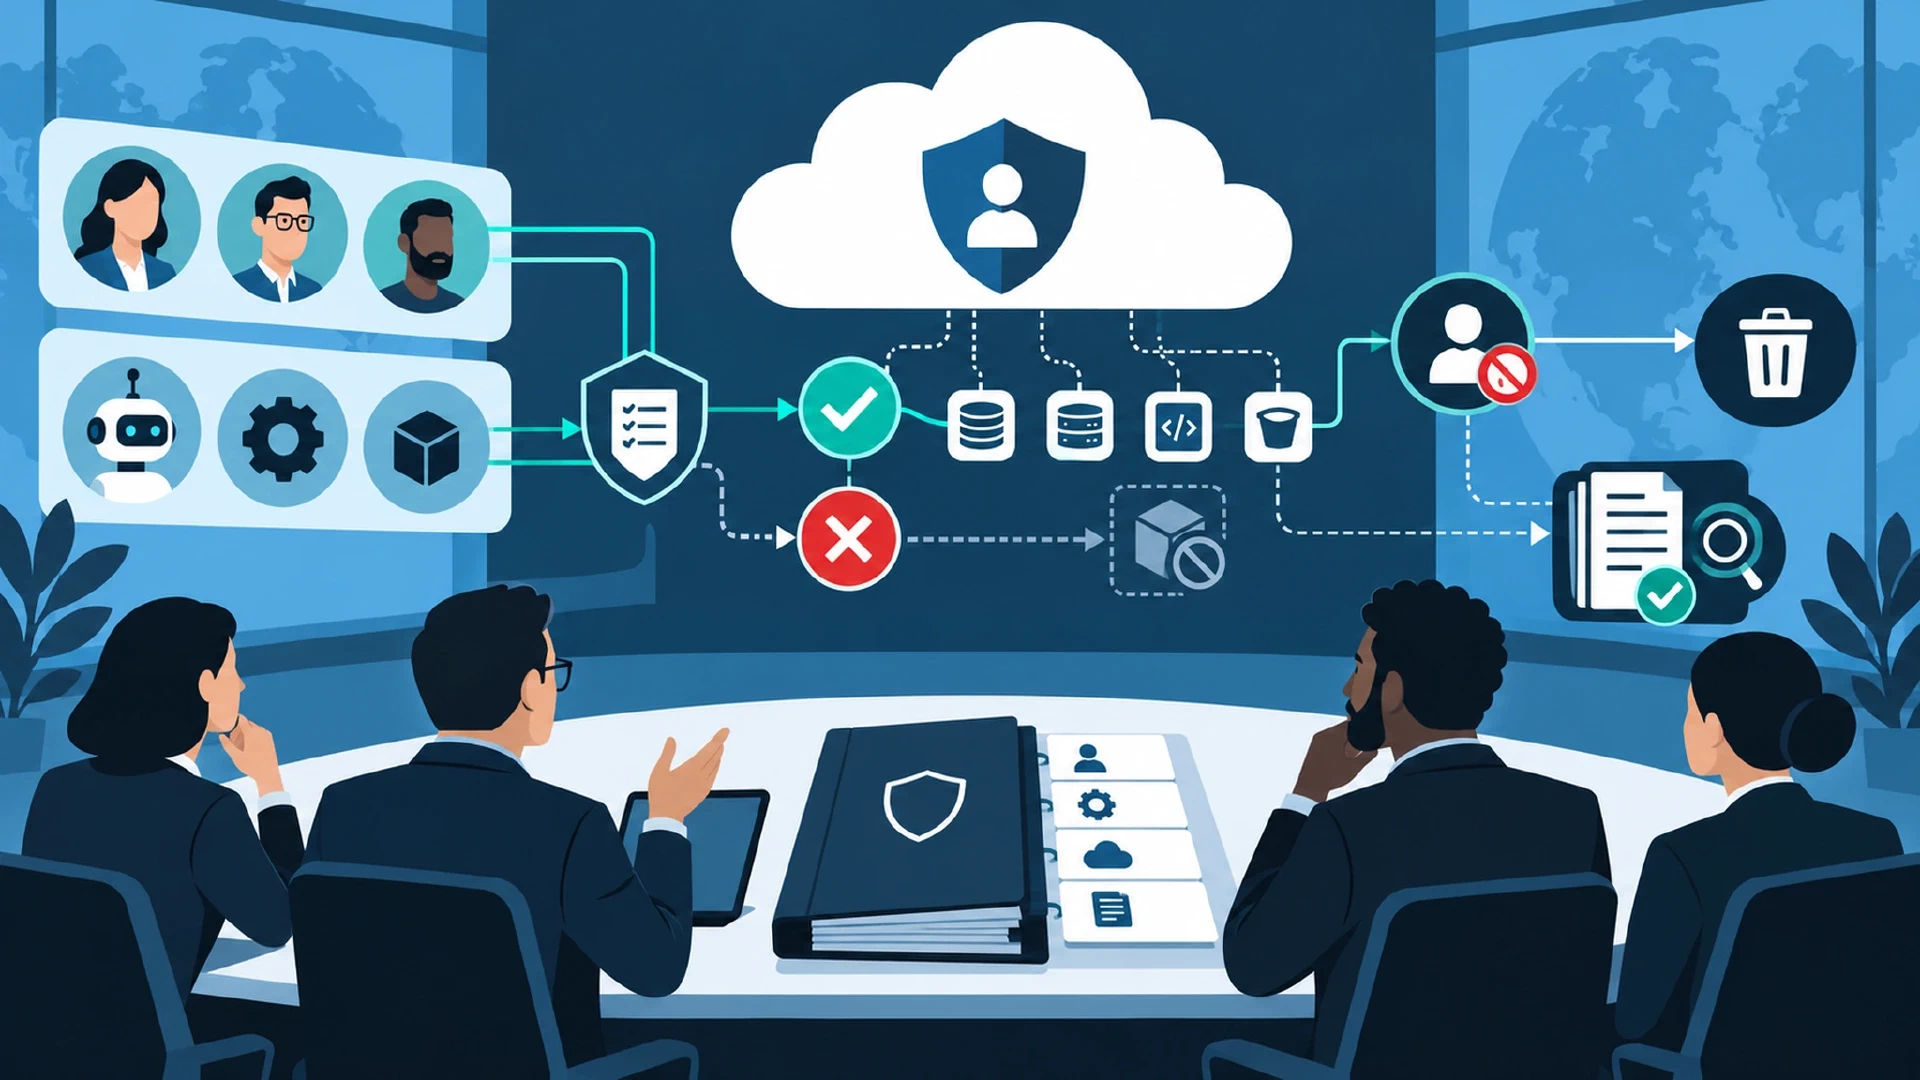
Review synthetic cloud access, design a least-privilege target state, test the offline simulator or a provider sandbox, and submit closure evidence.
 Turn an access inventory into a tested target state.#access review
Review the Cloud IAM and Zero Trust capstone reference design, evidence boundaries, simulator results, migration order, and scoring requirements.
 Compare the submitted package with the reference evidence.#access review
Design, test, review, and remove cloud identity access across AWS, Azure, and Google Cloud with zero trust principles and disposable labs.
 Grant narrow access, test the result, and remove the lab.#Least Privilege
#access review
Design federated human access with strong authentication, short sessions, privileged activation, emergency recovery, and continuous review.
 Give people temporary access tied to a verified identity.#privileged access
#access review