CompTIA Security+ (SY0-701): Security Architecture
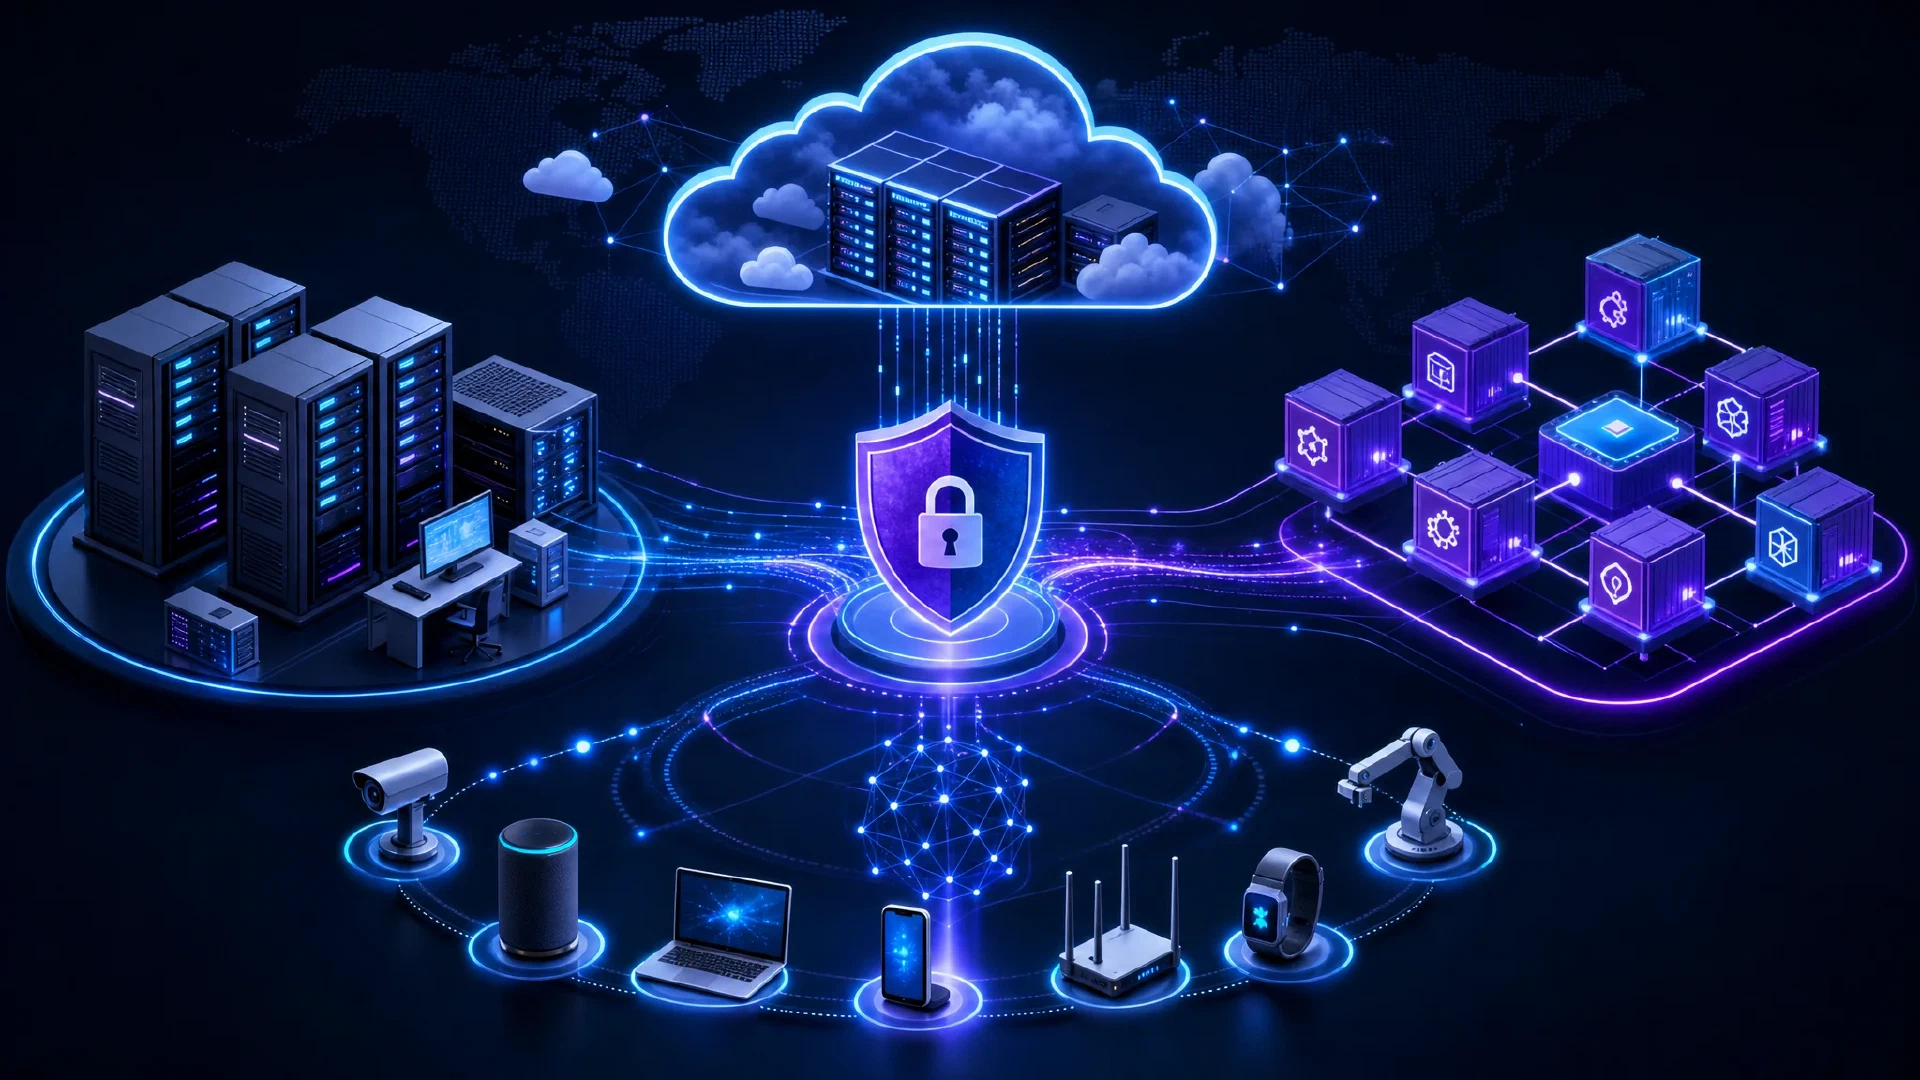
Table of Contents
Click Here to Return To the CompTIA Security+ Course Page
Security Architecture is 18% of the CompTIA Security+ (SY0-701) exam. This module covers how you design secure infrastructure, protect data across its states, and build systems that survive failure. Architecture choices decide how resilient your environment stays under attack.
You apply the concepts from Domain 1 to real designs here. You weigh trade-offs between cloud and on-premises, segment networks, encrypt data, and plan recovery before an incident forces your hand.
Architecture Models
Each model shifts cost, control, and responsibility differently.
| Model | Strength | Trade-off |
|---|---|---|
| On-premises | More direct control of owned hardware | You operate and patch what you own or contract to manage |
| Cloud | Capacity and managed services depend on the offering | Responsibility and visibility vary by service model |
| Hybrid | Combines selected local and hosted services | Needs explicit identity, routing, and ownership boundaries |
| Edge | Processing near a user or device can reduce latency | Distributed devices need lifecycle and access controls |
You also design with microservices, serverless, and Infrastructure as Code (IaC). IaC lets you version and review infrastructure the same way you review code. Embedded systems like IoT, ICS/SCADA, and RTOS may have constrained maintenance windows, so inventory and segment them according to their actual risk.
Cloud Security and Shared Responsibility
Cloud duties vary by service model and contract. In a typical infrastructure service, the provider operates underlying facilities and hardware, while the customer manages data, identities, operating systems, and configuration. Managed services shift some tasks to the provider, but the customer still owns access and data decisions.
- CASB (Cloud Access Security Broker) enforces policy between users and cloud apps.
- SASE converges networking and security capabilities delivered as a service.
- A public storage bucket exposes data when access rules are wrong. Review configuration and test access before release.
Compare the major platforms in AWS vs Azure vs Google Cloud Platform .
Infrastructure Security
You reduce the attack surface with placement and segmentation.
- Security zones group systems by trust level (DMZ, internal, restricted).
- VLANs and subnets separate traffic at Layer 2 and Layer 3.
- Zero Trust removes implicit trust and verifies every request.
- Network access control (NAC) checks device health before granting access.
Firewalls come in several types:
| Firewall | Inspects |
|---|---|
| Layer 4 (stateful) | Ports and connection state |
| NGFW | Applications, users, and deep packets |
| WAF | Web application traffic (XSS, SQLi) |
| UTM | Many functions in one appliance |
Place an IDS to detect and an IPS to block. Use DNSSEC to authenticate DNS data. It does not encrypt queries. Study vendor designs in Fortinet vs Cisco network security comparison and pfSense vs Firewalla .
Virtualization and Containerization
Virtual machines and containers share a host, so isolation matters.
- A hypervisor runs VMs, and VM escape is the worst-case breach.
- Containers share the host kernel, so a kernel flaw can spread.
- Scan images, sign them, and run with least privilege.
See Docker vs VMs for the practical differences.
Protecting Data
You match the control to the data state.
| State | Risk | Control |
|---|---|---|
| At rest | Stolen disk or backup | Full-disk and database encryption |
| In transit | Network sniffing | TLS, IPSec, VPN |
| In use | Memory scraping | Access control, secure enclaves |
You also obscure data:
- Encryption makes data unreadable without a key.
- Hashing creates a one-way fingerprint for integrity.
- Masking hides part of a value (showing only the last four digits).
- Tokenization swaps data for a non-sensitive token.
Resilience and Recovery
You design for failure before it happens.
- Redundancy removes single points of failure (RAID, dual power, NIC teaming).
- Load balancing spreads traffic across servers for uptime.
- Replication keeps live copies of data across sites.
- High availability (HA) keeps service running through clustering and failover.
Recovery sites trade speed for cost:
| Site | Recovery speed | Cost |
|---|---|---|
| Hot | Minutes | Highest |
| Warm | Hours | Medium |
| Cold | Days | Lowest |
Test backups with the 3-2-1 rule: three copies, two media types, one offsite. A restore test shows whether the backup meets the recovery need.
Practice: Draw and Test a Trust Boundary
Continue the Harbor Library case. The public catalog serves anonymous readers. Staff use a private records app and export member data. A cloud object store holds encrypted backups. Draw three zones: internet, staff, and restricted records. Mark the trust boundary and each permitted flow.
| Flow | Decision | Reason |
|---|---|---|
| Internet to public catalog on HTTPS | Allow | Readers need the catalog. |
| Internet to records database | Deny | No direct public access. |
| Staff app to records database on its required port | Allow for the app identity only | The app needs a narrow path. |
| Backup worker to object store | Allow for backup identity only | The worker needs write access. |
| Anonymous user to backup object | Deny | Backups contain restricted data. |
Now write one misconfiguration to look for in an infrastructure change, such as a bucket policy which grants public read. Explain the review gate and a negative access test. Do not deploy a public bucket to practice. A rule diagram and a written test are enough.
Assign cloud responsibilities to the provider or library: physical data-center security belongs to the provider; library identities, data classification, bucket policy, and restore checks belong to the library. The exact split depends on the service model. Encrypt the export at rest and in transit. Document who controls keys and who is allowed to decrypt.
Choose a recovery target: restore member records within 8 hours with no more than 24 hours of lost changes. These are fictional RTO and RPO requirements. Create a daily backup schedule, an offsite copy, and a monthly test restore to an isolated location. Record start time, finish time, recovered timestamp, file count, access check, and failed steps. RAID and replication improve availability but can copy corruption or deletion. They do not replace a recoverable backup.
Pass when your diagram shows no public path to the records database, your matrix assigns six controls or duties to an owner, and your restore evidence would show whether both targets were met.
References: CompTIA SY0-701 exam objectives and NIST Cybersecurity Framework 2.0 .
Worked design and score key
Internet -> public catalog
Internet -X-> records database
Staff PC -> staff app -> records database
Backup worker -> encrypted backup object
Anonymous user -X-> backup object
The arrows show permitted flows. -X-> means the intended policy denies the path. A diagram alone does not prove a firewall or bucket rule works. A completed ownership matrix assigns the public-catalog rule to network operations, staff-app identity to IAM, database access to the records owner, backup-worker identity to IAM, object-store policy to the cloud owner, and restore tests to the backup owner.
Example negative test record: 2026-10-10 10:00 UTC, synthetic anonymous request to backup object, expected access denied, observed not run, evidence none, owner Cloud lead. Do not replace not run with an invented HTTP status. A completed live lab must save the actual request and response with secrets removed.
Example recovery worksheet: latest healthy backup timestamp Friday 00:00, outage Saturday 00:00, isolated restore finishes Saturday 06:00. The 6-hour restore meets an 8-hour RTO, but the backup is 24 hours old, exactly at the 24-hour RPO limit. If the outage started Saturday 03:00 instead, the 27-hour gap would fail the RPO. A backup file count and one valid read after restore are needed before declaring success. These times are hypothetical and do not prove a real restore.
Award one point each for separated trust zones, complete allow/deny rules, six assigned owners, clear positive and negative access tests, correct RTO/RPO arithmetic, and honest observed/unrun status. Pass at 6 of 6 for the synthetic design. Real operations also need an isolated restore and access evidence.
Next Steps
Operate this architecture securely in Security Operations , and govern it through Security Program Management and Oversight . Review the basics in General Security Concepts , then return to the CompTIA Security+ Course .