en

STS Collective — cybersecurity apparel and gear
Shop Now — Save up to 20% Today Code: SIMEONONSECURITY
STS Collective — cybersecurity apparel and gear
Shop Now — Save up to 20% Code: SIMEONONSECURITY

Red-Team-Courses

Everything required before an attack: scope and rules of engagement, deconfliction, hardening the attack platform, standing up redirectors, and validating the infrastructure before go.

The networking and Active Directory concepts every red team technique builds on: HTTP and HTTPS, TCP and UDP, the domain controller, users, groups, and group nesting.

How Windows stores configuration and credentials: the registry and hives, registry paths, NTLM hashes, and the difference between domain and local authentication.
Follow C2 task delivery, polling latency, uncertain outcomes, and operator handovers through worked examples and a task-ledger exercise.

Understand BOF file formats, architecture compatibility, client integration, runtime limits, and failure boundaries through a benign test design.

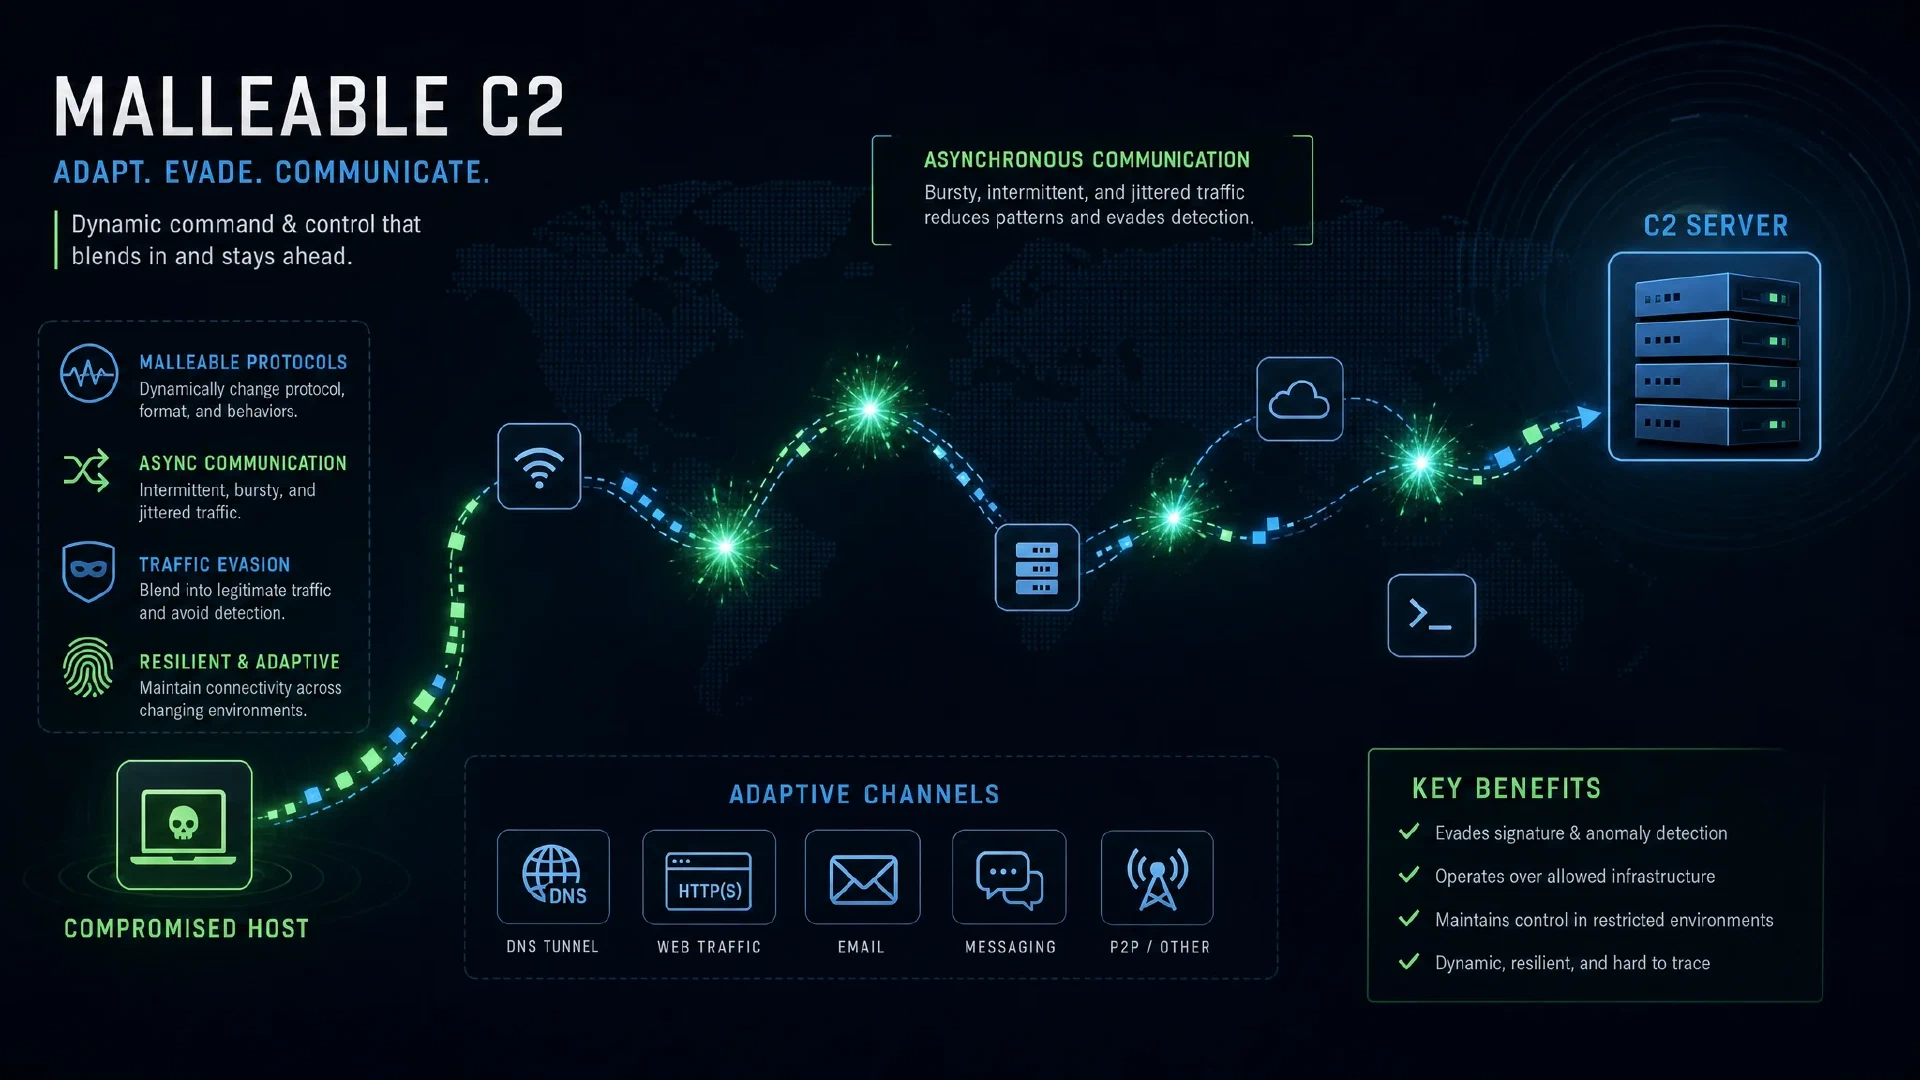
Separate profile validity, working communication, telemetry, and detection with a local HTTP exercise and controlled comparison record.

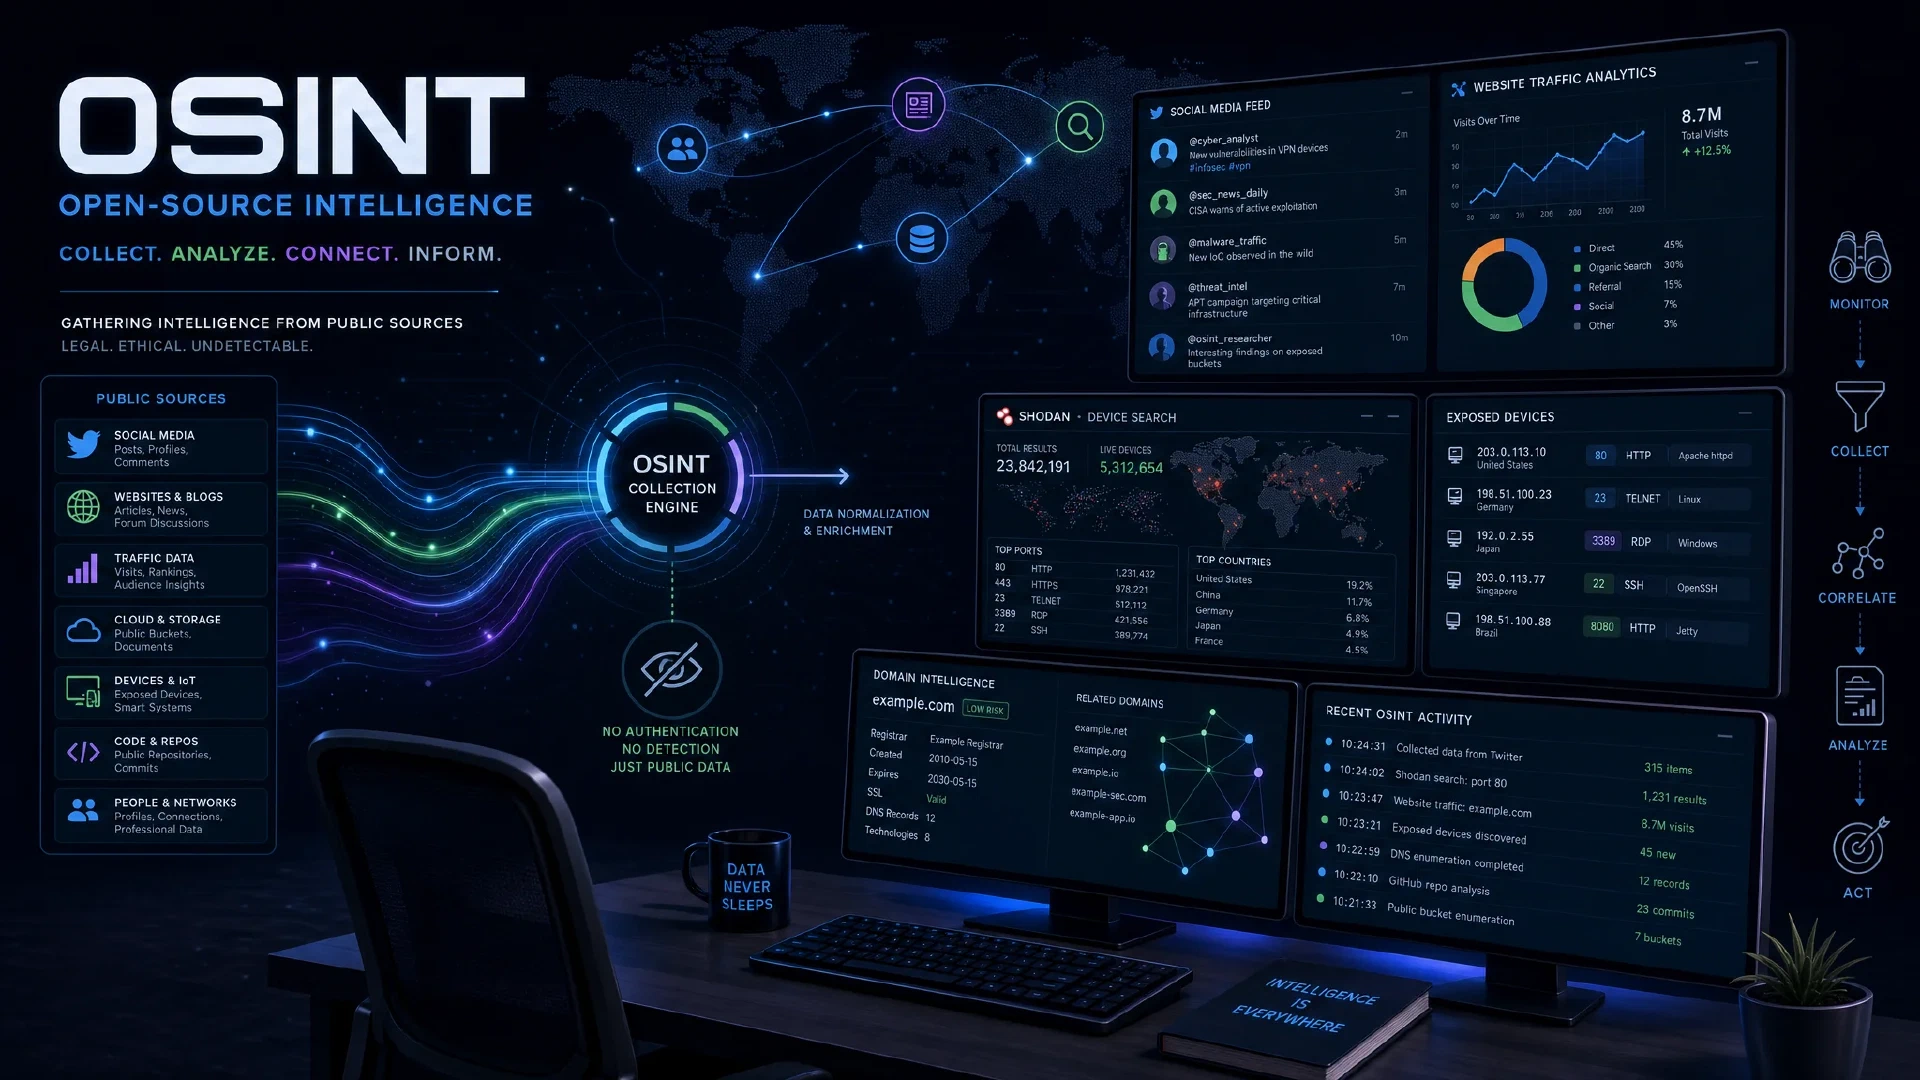
Evaluate public sources, RDAP, DNS, certificate logs, and scan data. Build a traceable OSINT brief with worked examples and source-quality checks.

Interpret Nmap port states, scan methods, and vantage points through a loopback exercise, segmentation case, and evidence-based scan plan.

STS Collective — cybersecurity apparel and gear
Shop Now — Save up to 20% Today Code: SIMEONONSECURITY