CompTIA Certification Roadmap: A+ to SecurityX
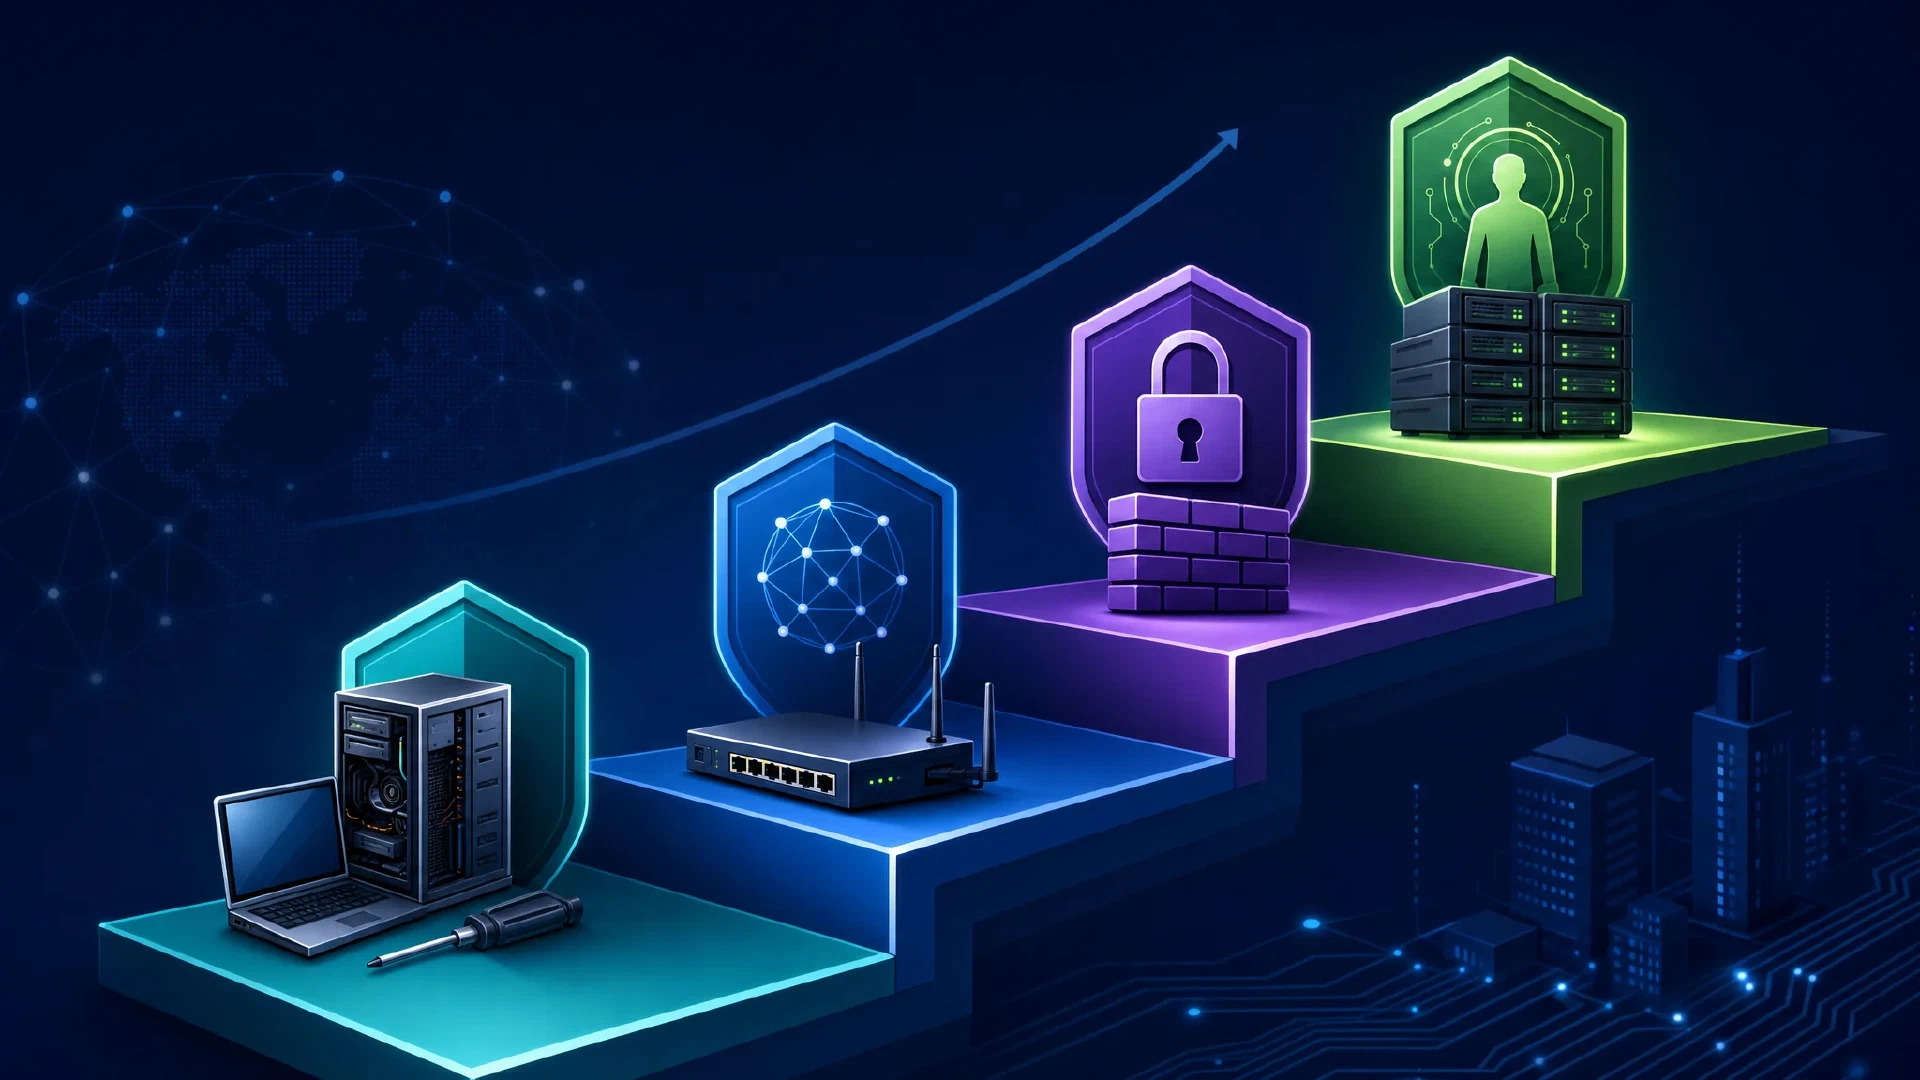
Table of Contents
Click Here to Return To the IT Career Playbook
CompTIA offers vendor-neutral credentials across IT support, networking, security, and Linux. Check job postings for the role and location you want before paying for an exam. A credential documents assessed knowledge. It does not replace work samples or experience.
Check each credential’s current renewal rules with CompTIA. Many use a three-year continuing education cycle, but accepted activities and automatic renewals differ by credential.
The CompTIA Certification Stack
| Certification | Exam Code | Level | What It Proves |
|---|---|---|---|
| CompTIA A+ | 220-1201 / 220-1202 | Entry | Hardware, OS, networking basics, troubleshooting |
| CompTIA Network+ | N10-009 | Entry/Intermediate | Networking infrastructure, protocols, troubleshooting |
| CompTIA Security+ | SY0-701 | Entry/Intermediate | Security fundamentals, threats, cryptography, compliance |
| CompTIA Linux+ | XK0-006 | Intermediate | Linux administration, services, scripting, troubleshooting |
| CompTIA CySA+ | CS0-004 | Intermediate | Cybersecurity analysis, threat detection, incident response |
| CompTIA PenTest+ | PT0-003 | Intermediate | Penetration testing methodology |
| CompTIA SecurityX | CAS-005 | Advanced | Enterprise security architecture, risk management |
| CompTIA SecAI+ | CY0-001 | Intermediate | AI security, AI systems integration |
| CompTIA SecOT+ | Draft SOT-001 | Pre-release | Operational technology security topics, subject to final objectives |
CompTIA A+ (220-1201 / 220-1202)
CompTIA A+ provides a starting point for many IT support paths. Federal work roles have specific qualification requirements under the DoD 8140 program. Check the applicable role and component before treating one credential as sufficient.
- Two exams required: Core 1 (220-1201) covers mobile devices, networking, hardware, virtualization, and cloud; Core 2 (220-1202) covers operating systems, security, software troubleshooting, and operational procedures.
- Study plan: map each official objective to a lesson, a lab, and a check result
- Resources: compare current exam codes and outlines before using a course or practice bank
See the full course on this site: CompTIA A+ Course (220-1201 / 220-1202)
CompTIA Network+ (N10-009)
CompTIA Network+ assesses networking concepts across vendor environments. Compare its scope with role requirements and other networking credentials before choosing an exam.
- Topics: Networking concepts, infrastructure, operations, security, network troubleshooting
- Study plan: build and troubleshoot a small network, then check gaps against N10-009 objectives
See the full course on this site: CompTIA Network+ Course (N10-009)
CompTIA Security+ (SY0-701)
CompTIA Security+ assesses foundational security concepts. Employers and federal components set different role qualifications. For DoD positions, use the current 8140 work-role matrix and the hiring component’s requirements rather than the former 8570 IAT levels.
- Topics: Attacks and threats, architecture, implementation, operations, governance, risk, compliance
- Study plan: complete a control, incident, and risk exercise, then check gaps against SY0-701 objectives
See the full course on this site: CompTIA Security+ Course (SY0-701)
CompTIA Linux+ (XK0-006)
CompTIA Linux+ covers Linux administration at a level suitable for sysadmin and cloud engineering roles. Unlike Red Hat’s RHCSA, it is vendor-neutral and covers multiple distributions.
- Topics: System management, services and users, security, automation and scripting, troubleshooting
- Study plan: document a Linux VM’s storage, services, users, security, automation, and troubleshooting evidence
See the course path: CompTIA Linux+ XK0-006
CompTIA CySA+ (CS0-004)
CompTIA CySA+ targets security analysts, SOC analysts, and IT professionals taking on security responsibilities. It focuses on threat intelligence, vulnerability management, and behavioral analytics.
- Topics: Threat intelligence, vulnerability management, incident response, reporting
- Study plan: produce a detection, vulnerability triage, response, and reporting record
- Federal roles: Check the current DoD 8140 work-role matrix and your component’s rules before choosing this credential for a position
See the course path: CompTIA CySA+ CS0-004
CompTIA PenTest+ (PT0-003)
CompTIA PenTest+ covers penetration testing methodology and is positioned between Security+ and the Offensive Security OSCP. It is vendor-neutral and emphasizes both technical and reporting skills.
See the full course on this site: CompTIA PenTest+ Course (PT0-003)
CompTIA SecurityX (CAS-005)
CompTIA SecurityX (formerly CASP+) is an advanced security certification for practitioners. It requires renewal under CompTIA’s continuing education program. Check the current SecurityX renewal options and the applicable DoD 8140 work-role matrix before planning a credential path.
See the course path: CompTIA SecurityX CAS-005
Recommended Study Sequence
A structured progression for an IT professional targeting a security-aware sysadmin or cloud role:
- CompTIA A+ — hardware and OS fundamentals
- CompTIA Network+ — networking
- CompTIA Security+ — security baseline
- Branch based on specialization:
- Sysadmin/Cloud path: Linux+ then cloud certs
- Security path: CySA+ then consider CISSP
- Networking path: Cisco CCNA (see Cisco Certifications Guide )
Do not stack certifications too fast without applying skills at work or in a home lab. Certifications without experience have diminishing returns.
Next Steps
- Cloud Certifications Guide
- Cisco Networking Certifications
- IT Training Resources Online
- IT Career Playbook Home