CEH v13: Sniffing
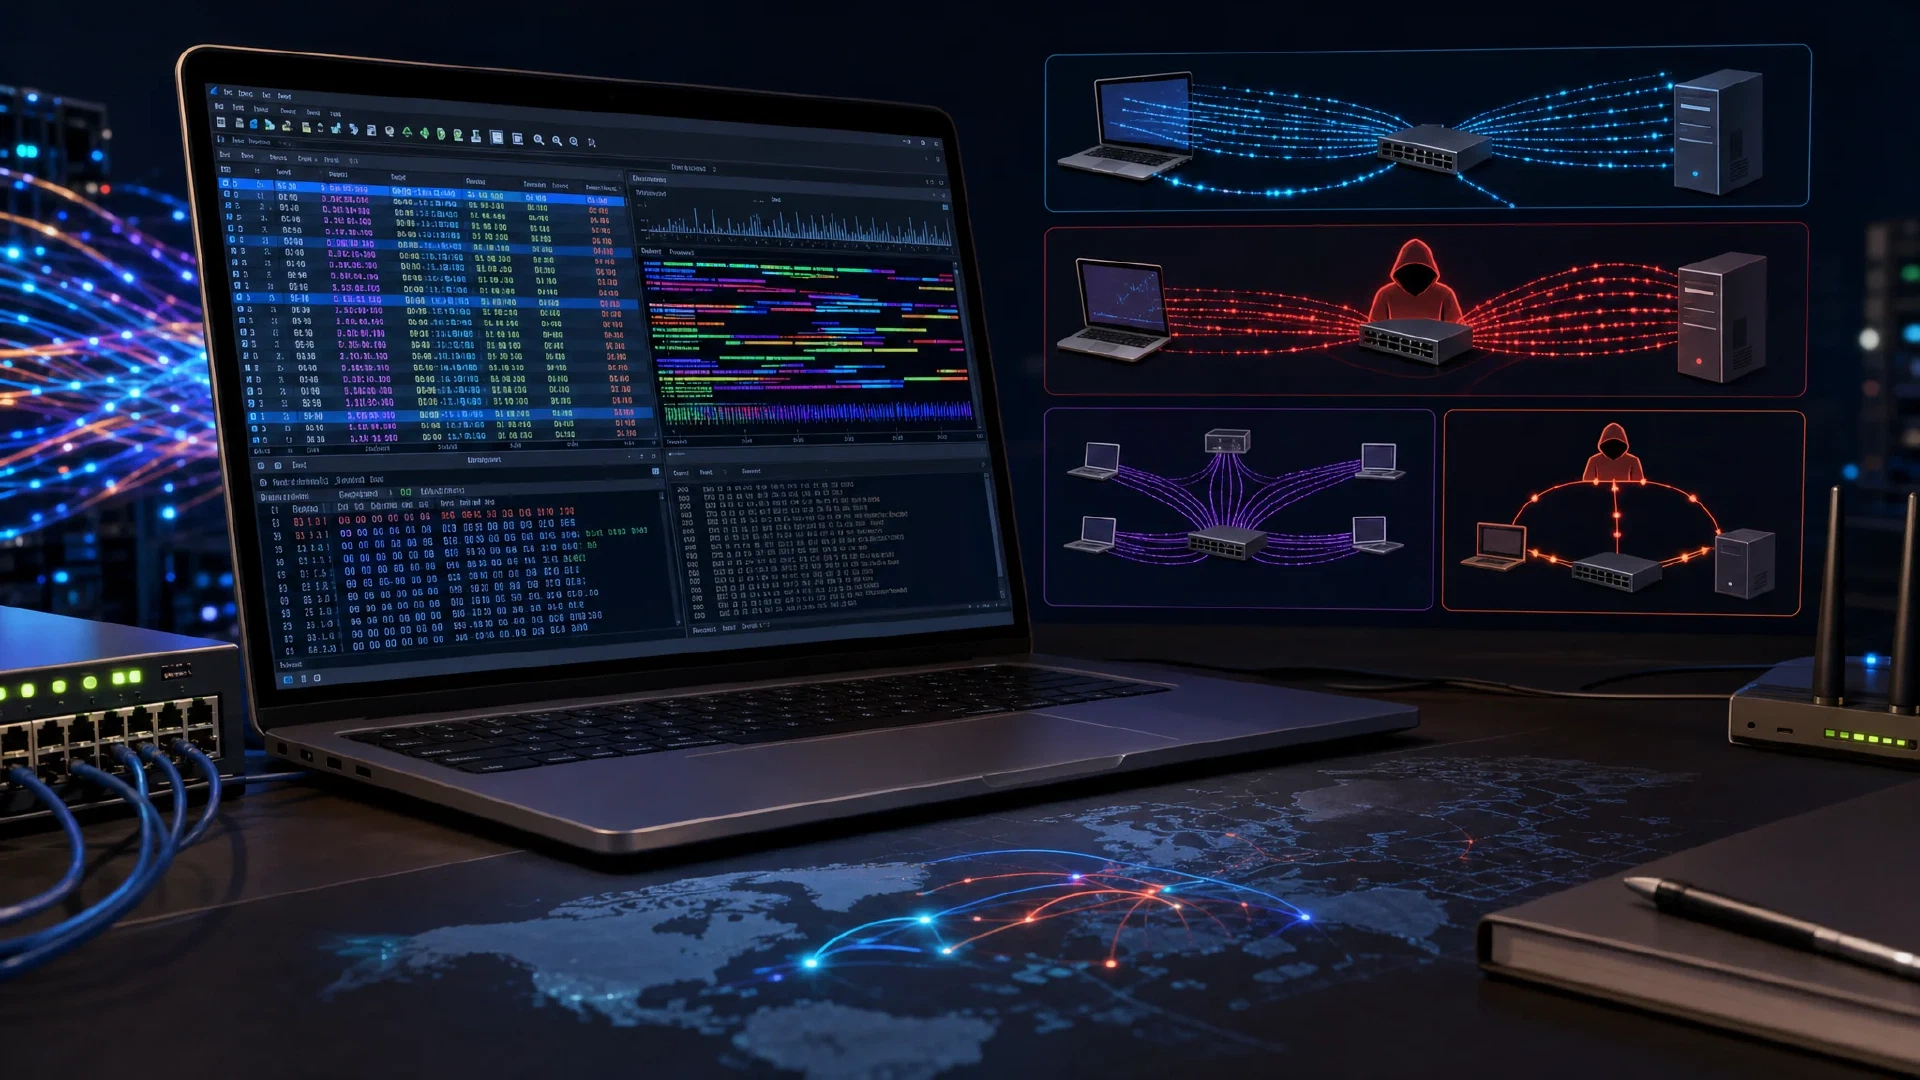
Table of Contents
Click Here to Return To the Certified Ethical Hacker (CEH v13) Course Page
Sniffing captures and analyzes network traffic in the EC-Council CEH v13 course. This module covers passive and active sniffing, switch-based attacks, and the tools that read packets off the wire. Capture traffic only on networks you are authorized to test.
A sniffer reads packets as they cross the network. On unencrypted protocols this exposes credentials, session tokens, and sensitive data in plaintext.
Passive vs. Active Sniffing
The network design decides which approach works.
| Type | Where it works | Method |
|---|---|---|
| Passive | Hubs, mirrored ports | Listens without altering traffic |
| Active | Switched networks | Forces traffic to your host |
Switches send traffic only to the right port, so an attacker uses active techniques to redirect it.
Active Sniffing Attacks
You manipulate Layer 2 to intercept traffic.
- ARP poisoning sends forged ARP replies so victims send traffic through you. This is a man-in-the-middle position.
- MAC flooding tries to exhaust a switch’s MAC table. Some switches then flood unknown unicast traffic, while others rate-limit or protect the port. The result depends on the device and configuration.
- DHCP starvation exhausts the DHCP pool, then a rogue server hands out malicious settings.
# Capture traffic on an interface and filter for HTTP
sudo tcpdump -i eth0 -A 'tcp port 80'
Analysis Tools
| Tool | Use |
|---|---|
| Wireshark | Deep graphical packet analysis |
| tcpdump | Command-line capture and filtering |
| Ettercap | Man-in-the-middle and ARP poisoning |
| dsniff | Extracts credentials from traffic |
You apply display filters in Wireshark like http.request or tcp.port == 443 to focus on relevant packets.
Countermeasures
You defend against sniffing with encryption and switch hardening.
- Encrypt traffic with TLS, SSH, and VPNs so captured data stays unreadable.
- Dynamic ARP Inspection (DAI) validates ARP packets against trusted bindings where configured. It helps block spoofed ARP traffic, but needs correct DHCP snooping bindings or approved static entries.
- Port security limits MAC addresses per port to stop flooding.
Encryption limits what a passive sniffer reads. Captured ciphertext still exposes metadata such as endpoints, timing, and volume, and poor key management or compromised endpoints create other paths to the data.
Next Steps
Move from technical capture to human attacks in Social Engineering . Revisit malicious code in Malware Threats . Return to the Certified Ethical Hacker (CEH v13) Course .